Understand the incident
Review visible symptoms and available evidence. We identify affected files, users and components as access and hosting conditions allow.
Unexpected redirects, unknown administrator accounts, suspicious files and browser warnings can signal a compromised website. WordPress virus removal and malware removal are part of the same recovery work: investigate what happened, remove the infection and address the way it got in.
Request a project quote ↗
For owners of compromised WordPress websites and WooCommerce stores, or anyone seeing security warnings, injected pages or suspicious changes.
Review visible symptoms and available evidence. We identify affected files, users and components as access and hosting conditions allow.
Remove confirmed malicious content or restore suitable clean files. Recovery steps depend on the extent of the compromise and the quality of available backups.
Review the vulnerable components and access that contributed to the incident. Update, replace or remove affected software as agreed.
A clearer recovery process when WordPress feels out of control. These are the situations we discuss with you before recommending a scope.
Suspicious redirects, pop-ups and browser warnings can damage confidence in your business. The visible symptom may not reveal which file, account or extension allowed the compromise, leaving you unsure what to do next.
We assess the reported behaviour and relevant installation components, identify the required recovery access and agree the cleanup scope. Available containment options and hosting restrictions are discussed before work begins.
Removing an obvious injected file can leave altered content, another compromised file or an unauthorised account behind. Unsupported software or exposed credentials may also leave the original entry point open.
Recovery includes reviewing the affected areas within scope, investigating likely entry points and recommending software or access changes. We explain findings and remaining uncertainties rather than treating the disappearance of one symptom as the whole assessment.
A backup can be older than expected or already contain unwanted changes. Restoring it without considering important business data and the incident timeline can replace one problem with another.
We discuss backup dates, recent changes and the information that must be preserved. The recovery plan explains whether cleanup, restoration or another approach is appropriate and which checks should follow.
The starting point is the symptoms, their timing and the access available. Hosting notices, affected URLs and examples of unwanted behaviour help define the investigation. Please keep credentials and sensitive customer information out of the public form. Access and live-site changes are coordinated through an agreed handover.
Recovery is scoped around the condition of the installation. Work can include reviewing WordPress files, themes, plugins, database content and user accounts, replacing or cleaning affected components and checking the reported behaviour. Backup availability, missing licences and unsupported software influence the plan. We explain these factors before making a recovery commitment.
After cleanup, we review the agreed journeys and document follow-up actions. Hosting restrictions and search security warnings may require separate provider review; their approval timelines remain outside our control. Credential changes, component replacement and ongoing care responsibilities are agreed so the next stage is clearer than the incident itself.
Discuss this work with TechieIQ ↗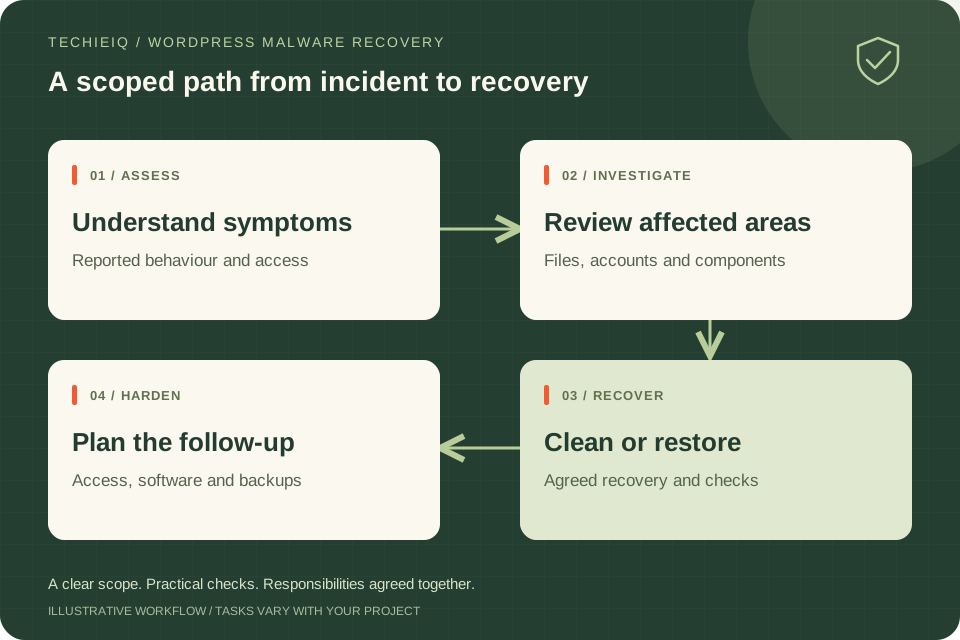
Here is how we apply the relevant technical work to your project. Ask us to walk through the approach and discuss examples that can be shared during your consultation.
We connect symptoms with relevant files, accounts and extensions. The objective is to understand the affected scope and likely weaknesses rather than assume every redirect has the same cause. Investigation depth and any evidence-preservation requirements are discussed before work starts.
We review whether affected components should be cleaned, replaced from a trusted source or restored from a suitable backup. Changes are coordinated with the owner and host. Missing source files, premium licences and unavailable backups are identified as practical constraints rather than hidden assumptions.
Recommendations address access ownership, credentials, supported software and backups according to the findings. Routine care can then organise ongoing maintenance. No cleanup can guarantee the website will never be attacked again, so remaining risks and responsibilities are documented.
We agree review points before implementation, so you can understand what the work covers and how it will be handed over. These are typical items we discuss when preparing your proposal.
Recovery time depends on access, infection scope, software condition and backups. Specialist forensics, legal incident handling and independent assurance are separate unless specifically arranged. A fixed cleanup time is not promised before assessment.
These are the typical areas we discuss for this service. Your written proposal confirms exactly what is included, the milestones and the cost. Third-party subscriptions, licences and services are identified separately.
Ask about this service on WhatsApp ↗Share the symptoms and website address; we discuss access and urgency.
Assess the affected site and agree the cleanup scope.
Clean or restore the site and review the likely entry points.
Check key pages and provide a recovery summary and next steps.
Send your site URL, screenshots of warnings, when the problem began and any recent changes. Avoid installing more cleanup tools or deleting evidence before assessment if you can safely pause changes.
An infection may involve altered core files, compromised plugins, injected database content or unauthorised accounts. Removing one visible symptom may leave another entry point in place. We assess the site as a whole within the agreed scope, explain the findings and recommend action on affected components and access.
A recovered website still needs current software, protected accounts and a sensible backup routine. Hosting restrictions, search warnings or third-party review processes may also need follow-up. We explain which checks were completed and which actions remain with you or another provider. Ongoing maintenance can be discussed after the immediate incident is addressed.
Choose the tools for the outcome you need. We review your existing setup and explain compatibility, access and support responsibilities before work begins.
Review core files, users, themes and plugins for signs of compromise.
Review store access and checkout behaviour as part of the recovery scope.
Investigate affected files and database content within the agreed assessment.
Review entry points, backups and server access with your provider.
We work digitally with businesses across India and worldwide. Tell us what you need, and we will explain the next step.
The time depends on access, the size of the infection, hosting restrictions and available backups. We discuss an estimate after the initial assessment.
We can help resolve the website issue and guide the review request. Removal of a warning depends on the relevant provider and its review process.
No. We can address identified weaknesses and recommend ongoing controls. Continued updates, protected credentials and safe hosting practices remain necessary.
Tell us whether you need a new website, a repair, an online store or ongoing maintenance. Share your current website address if you have one. We will review your request and contact you to discuss the scope.
◉ Chat on WhatsApp ↗[email protected]Online consultations · India & international projects